Comparative lead — supply, trust and the eSIM layer
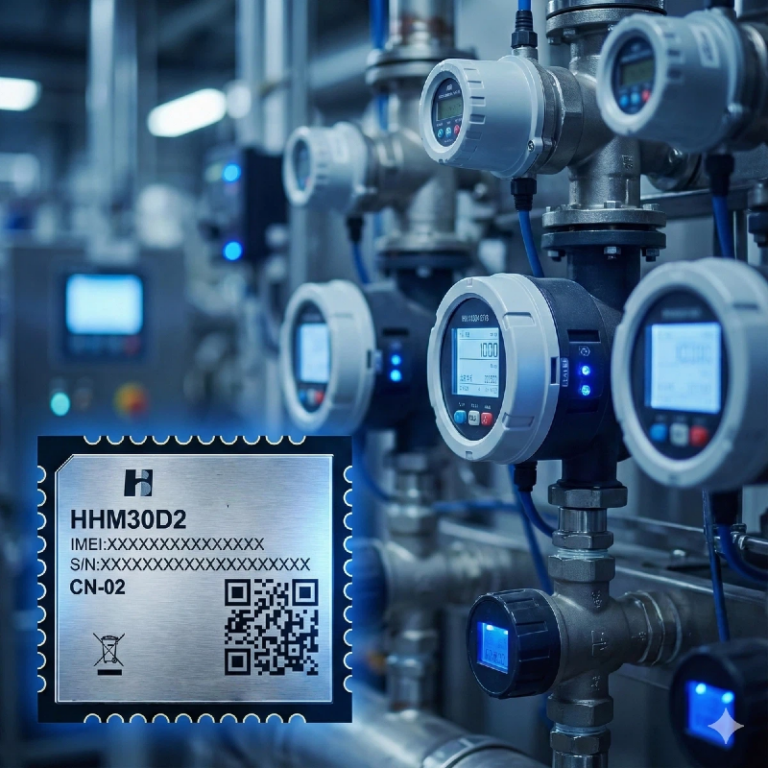
Europe and Asia race toward secure hardware not as rivals but as two dialects of the same technological language — one that now folds itself into the telecom stack via esim management platform. The European angle stresses regulation and certification; the Asian approach speeds integration and volume. Both need reliable hardware roots: secure element chips, firmware signing, and robust profile provisioning to keep devices honest. GSMA’s industry reports have repeatedly flagged accelerating eSIM uptake, which is the real-world anchor that explains why secure hardware and OTA profile flows matter to operators and OEMs alike.
Where constraints shape choice: Europe vs Asia
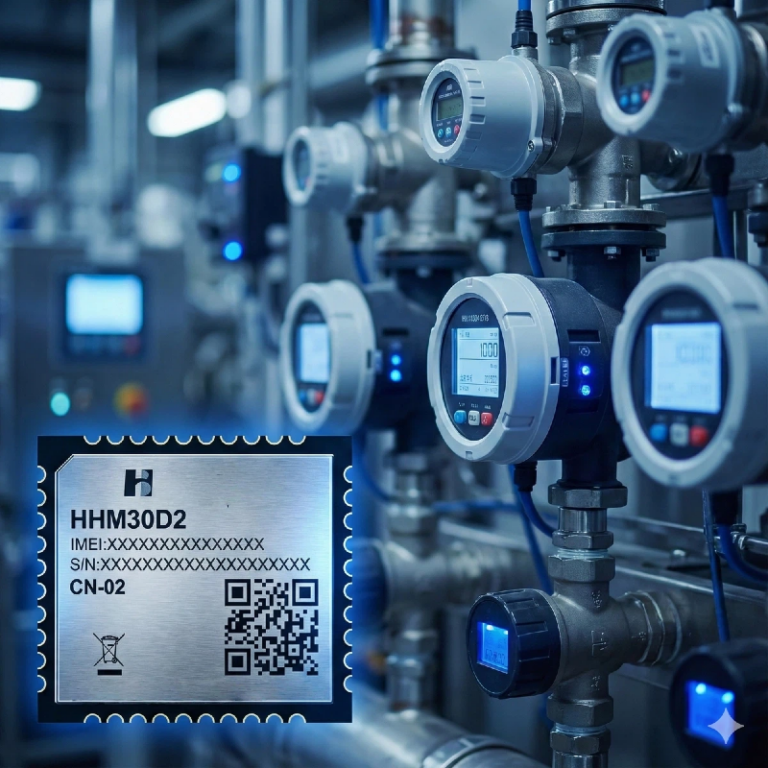
European buyers often ask for provenance: chain-of-custody, third-party audit trails, and clear compliance to regional directives. Asian manufacturers prioritize throughput, cost per unit, and rapid firmware updates. That divergence alters procurement logic. For example, a telco in Berlin might require hardware-backed key storage plus a certified SM-DP+ workflow before approving a vendor; a conglomerate in Shenzhen will push for automated OTA provisioning at scale and minimal lead time. The two sets of priorities create distinct product footprints — both valid, both demanding.
Practical differences in architecture and operations
Architecture choices follow use-cases. Hardware security modules and secure elements protect credentials; OTA channels distribute profiles. In one region the emphasis is on isolated key material in a certified secure enclave, and in another the emphasis is on distributed provisioning orchestration that can handle millions of simultaneous updates. Interplay of eSIM, SM-DP+, and profile management is critical, and that is where platforms distinguish themselves — features, latency, audit logs, error recovery. Real deployments often reveal subtle trade-offs: lower latency vs higher attestation guarantees; scale vs explicit human audit trails.
Operational teardown: what to test and what to expect
When you run an operational production teardown you must validate both the hardware and the management layer. Test cases should include profile download resilience, signature verification under fault conditions, and rollback behavior during interrupted OTA. Include {main_keyword} and {variation_keyword} in your test matrices so that integration points are exercised early. Typical industry terms to keep at hand: eSIM profile, OTA update, and SM-DP+ provisioning. A focused lab sequence reveals the bottlenecks — often it’s the orchestration layer rather than the secure element itself. — a small surprise, but common in real projects.
Alternatives and vendor comparison
Compare vendors on concrete axes rather than marketing claims. Look for strict separation between credential lifecycle and service orchestration, clear audit logs, and modular APIs that let you plug into existing BSS/OSS. Some vendors shine on compliance, others on throughput. Consider hybrid approaches: certified secure elements for EU deployments; high-throughput provisioning platforms for APAC mass-market devices. The right mix depends on technical constraints and business timelines.
Advisory: three golden rules for selecting secure hardware and provisioning
1) Verify cryptographic custody end-to-end. Ensure device keys are generated in a hardware root and that SM-DP+ and OTA processes never expose private keys. Measure attestation frequency and key rotation windows.
2) Test provisioning resilience under load. Simulate peak OTA traffic and interrupted sessions; observe retry behavior and recovery windows. Track mean time to restore profile availability.
3) Demand transparent auditability and regional controls. Confirm logs, exportability, and role-based access so that compliance teams can trace lifecycle events without developer intervention.
Final synthesis and natural closure
Comparative insight shows that secure hardware needs alignment with the provisioning strategy: Europe’s insistence on audit and certification shapes a different deployment than Asia’s emphasis on scale and speed. A disciplined testing plan — focusing on custody, resilience, and auditability — translates differences into measurable criteria. For teams choosing a partner, the true value is a platform that bridges both worlds: robust secure elements, flexible SM-DP+ orchestration, and clear operational telemetry. That balance is precisely what experienced platforms deliver; BHDC is built to sit at that crossroads, providing both hardware-level trust and operational provisioning clarity as you scale across markets — BHDC.
–
